PUBLISHER: Mordor Intelligence | PRODUCT CODE: 2157030

PUBLISHER: Mordor Intelligence | PRODUCT CODE: 2157030
API Abuse Detection - Market Share Analysis, Industry Trends & Statistics, Growth Forecasts (2026 - 2031)
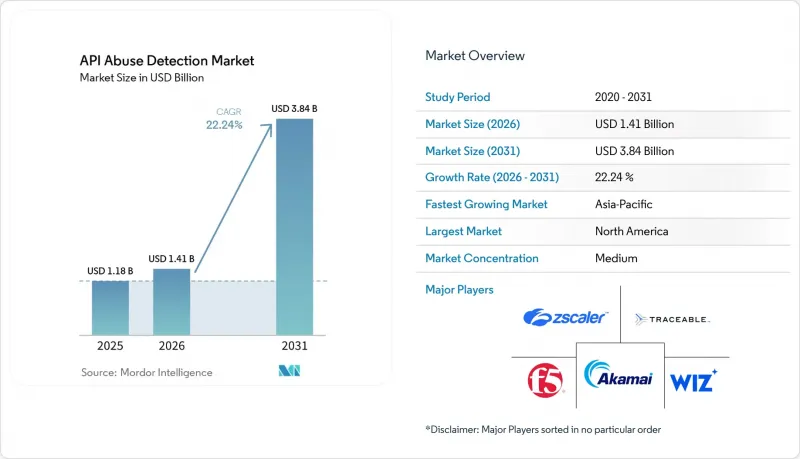
According to Mordor Intelligence, the API abuse detection market size is expected to grow from USD 1.18 billion in 2025 to USD 1.41 billion in 2026, and is forecast to reach USD 3.84 billion by 2031, at a 22.24% CAGR over 2026-2031.
Global API Abuse Detection Market Trends and Insights
Expansion of API-Enabled Digital Transactions
Organizations now use partner APIs and developer marketplaces to generate direct revenue. An API abuse event can therefore interrupt revenue and breach partner service commitments. Salt Security reported that, in 2026, 66% of organizations had increased their API count by more than 50% over the previous 12 months. Security teams must instrument a growing API estate while product teams release new services. This makes revenue assurance and service-level agreements relevant to procurement in the API abuse detection market. Financial services, logistics, and media organizations face this exposure, with API monetization already part of their operating models.
Rising Credential Stuffing and Account-Takeover Automation
Credential stuffing no longer depends only on predictable IP rotation or call-volume patterns. A 2025 open-banking study found that stronger rate limits and anomaly detection reduced operational tail losses by 20-30% against baseline cases. PCI DSS 4.0.1 became mandatory on March 31, 2025, requiring internet-facing payment systems to address automated credential attacks. Passwordless and token-based authentication increase the need to assess complete API sessions rather than only login endpoints. Behavioral profiling helps distinguish compromised activity from approved use with valid credentials. This requirement narrows the practical gap between traditional web application firewalls and dedicated API abuse detection platforms.
Fragmented API Ownership and Incomplete Asset Inventory
Asset visibility remains a basic limitation for API abuse detection. In the second half of 2025, 19% of security teams were very confident in the accuracy of their API inventory, while 25% were not very or not at all confident. Ownership is often divided among product engineering, platform, data, and partner integration teams. A complete register may not have a single accountable owner. Discovery is consequently becoming part of platform sales and can increase deal complexity. Akamai introduced Security Posture Center capabilities with code-to-runtime mapping to connect observed APIs with source repositories and recent committers. The API abuse detection market must address this discovery gap before runtime controls can cover all exposed interfaces.
Other drivers and restraints analyzed in the detailed report include:
- Regulatory Pressure for API Inventory and Resilience
- Growth of Cloud-Native and Microservices Architectures
- False Positives in Legitimate High-Volume Automation
For complete list of drivers and restraints, kindly check the Table Of Contents.
Segment Analysis
Solutions accounted for 68.12% of the API abuse detection market share in 2025. Enterprise buyers seek platforms with SIEM and SOAR connectors, behavioral baselining, policy enforcement, and centralized inventory management, functions that are difficult to reproduce through a services contract alone. The solutions category includes runtime protection, posture management, discovery, and business-logic anomaly detection, enabling buyers to cover the API attack surface through one procurement process. Cequence Security stated that its platform protects more than 10 billion daily API interactions. That operating scale shows why large customers prioritize reliable processing and low performance impact.
Services are projected to expand at a 25.03% CAGR through 2031. Managed security service models allow organizations to outsource monitoring to specialized security operations teams while professional services support DevSecOps integration and policy design. This approach is relevant to mid-sized businesses without a dedicated API security team, and 42Crunch surpassed 2 million tool downloads in November 2025 and expanded access through the Microsoft Security Store. Its freemium model shows how developer tools and advisory services can drive broader platform adoption. The API abuse detection industry uses these channels to help customers operationalize software after purchase.
Cloud deployment accounted for 61.33% of the API abuse detection market in 2025. Cloud platforms can scale with API traffic and connect with cloud identity services, while hybrid deployment is projected to grow at a 24.40% CAGR through 2031. It reflects the need to cover private data centers, public clouds, and colocation facilities, and to enable organizations to inspect internal service-mesh traffic on-premises while routing public APIs through cloud-delivered controls. This split can meet data residency, latency, and sovereignty needs. It also avoids treating one hosting model as sufficient for every workload.
On-premises deployment remains relevant where data rules prevent API traffic from entering an external inspection service. Defense contractors, central bank infrastructure, and critical infrastructure operators are key examples, and F5 launched the API Security Local Edition in 2026 for environments that require API visibility without external cloud connectivity. The release shows that on-premises and hybrid models remain durable for regulated enterprises, while some organizations are moving from fully local tools to hybrid architectures. That transition can broaden coverage for providers rather than simply replace an existing revenue source. The API abuse detection market is adapting to these mixed infrastructure choices.
Complete Report Scope:
- By Component
- Solutions
- Services
- By Deployment
- Cloud
- On-Premises
- Hybrid
- By Organization Size
- Large Enterprises
- Small and Medium-Sized Enterprises
- By API Type
- REST APIs
- GraphQL APIs
- SOAP APIs
- gRPC and Other APIs
- By Industry Vertical
- Government and Public Administration
- Industrial Manufacturing
- Retail and E-Commerce
- Transportation and Logistics
- Energy and Utilities
- Oil and Gas
- IT and Telecommunication
- Media and Entertainment
- Education and Research Institutions
- Healthcare and Life Sciences
- Banking, Financial Services, and Insurance (BFSI)
- Other Industry Verticals
- By Geography
- North America
- United States
- Canada
- Mexico
- South America
- Brazil
- Argentina
- Rest of South America
- Europe
- Germany
- United Kingdom
- France
- Italy
- BENELUX
- Rest of Europe
- Asia-Pacific
- China
- Japan
- India
- South Korea
- Australia
- Rest of Asia-Pacific
- Middle East and Africa
- Middle East
- United Arab Emirates
- Saudi Arabia
- Rest of Middle East
- Africa
- South Africa
- Nigeria
- Egypt
- Rest of Africa
- Middle East
- North America
Geography Analysis
North America held 36.19% of the API abuse detection market share in 2025. The region combines digital commerce infrastructure, regulated financial institutions, and mature enterprise security procurement, while U.S. consumer-facing platforms also face enforcement pressure around automated credential attacks and privacy. Canada's position follows banking modernization and alignment with U.S. enterprise procurement cycles, and South America remains an emerging area for adoption. Brazil's Open Finance framework has supported interoperability in open banking and drawn additional attention to fintech API protection.
Europe has a distinct demand profile because regulatory obligations are central to procurement, and BaFin began processing DORA notifications and third-party ICT registers on January 17, 2025. BAFIN.DE Germany's NIS2 legislation entered into force in December 2025 and widened resilience obligations, while the United Kingdom, France, and BENELUX benefit from financial services concentration and established DevSecOps adoption. EU open banking frameworks also sustain security demand in BFSI, providing a stable base for the API abuse detection market through the forecast period.
Asia-Pacific is projected to expand at a 23.60% CAGR through 2031. Akamai found that, in 2025, 85% of surveyed organizations in China, India, Japan, and Australia had experienced an API security incident in the prior 12 months. The same study reported an average estimated incident cost above USD 580,000 per event. IIJ launched its Raptor Behavioral Detection Solution for Japanese securities trading systems in June 2025. The Middle East and Africa are earlier-stage regions, with the UAE and Saudi Arabia supported by digital infrastructure programs. Mobile payment APIs in South Africa, Nigeria, and Egypt are an initial source of demand for detection tools.
- 42Crunch
- Akamai Technologies, Inc.
- Akto Security Inc.
- AppSentinels, Inc.
- APISec.ai, Inc.
- Arkose Labs Inc.
- Cequence Security, Inc.
- Cloudflare, Inc.
- Data Theorem, Inc.
- F5, Inc.
- Fastly, Inc.
- FireTail, Inc.
- Imperva, Inc.
- Indusface Private Limited
- Levo, Inc.
- Noname Security, Inc.
- Salt Security, Inc.
- SecureBlink, Inc.
- Traceable, Inc.
- Wallarm, Inc.
- Kong Inc.
- Wiz, Inc.
- Zimperium, Inc.
- Zscaler, Inc.
- Radware Ltd.
Additional Benefits:
- The market estimate (ME) sheet in Excel format
- 3 months of analyst support
TABLE OF CONTENTS
1 INTRODUCTION
- 1.1 Study Assumptions and Market Definition
- 1.2 Scope of the Study
2 RESEARCH METHODOLOGY
3 EXECUTIVE SUMMARY
4 MARKET LANDSCAPE
- 4.1 Market Overview
- 4.2 Impact of Macroeconomic Factors
- 4.3 Market Drivers
- 4.3.1 Expansion of API-Enabled Digital Transactions
- 4.3.2 Rising Credential Stuffing and Account-Takeover Automation
- 4.3.3 Regulatory Pressure for API Inventory and Resilience
- 4.3.4 Growth of Cloud-Native and Microservices Architectures
- 4.3.5 AI-Assisted Reconnaissance and Business-Logic Probing
- 4.3.6 API Abuse Detection Embedded in Fraud and Bot-Management Programs
- 4.4 Market Restraints
- 4.4.1 Fragmented API Ownership and Incomplete Asset Inventory
- 4.4.2 False Positives in Legitimate High-Volume Automation
- 4.4.3 Encrypted East-West Traffic and Observability Gaps
- 4.4.4 Integration and Skills Burden Across DevSecOps Toolchains
- 4.5 Value Chain Analysis
- 4.6 Regulatory Landscape
- 4.6.1 GDPR and Data Protection Requirements
- 4.6.2 PCI DSS 4.0.1 and Payment API Controls
- 4.6.3 DORA and Third-Party ICT Resilience
- 4.6.4 NIS2 and Critical-Entity Cybersecurity Duties
- 4.6.5 HIPAA and Protected Health Information
- 4.7 Technological Outlook
- 4.7.1 Behavioral Analytics and Entity Profiling
- 4.7.2 Positive Security Models and Schema Validation
- 4.7.3 GraphQL and gRPC Protection
- 4.7.4 Runtime Application Self-Protection and Service-Mesh Enforcement
- 4.7.5 AI-Agent, LLM and MCP API Protection
- 4.8 Porter's Five Forces Analysis
- 4.8.1 Threat of New Entrants
- 4.8.2 Bargaining Power of Suppliers
- 4.8.3 Bargaining Power of Buyers
- 4.8.4 Threat of Substitutes
- 4.8.5 Competitive Rivalry
- 4.9 Primary Abuse Use Case Analysis
- 4.9.1 Identity, Account and Session Abuse Detection
- 4.9.2 Business-Logic and Transaction Abuse Detection
- 4.9.3 Data Extraction, Scraping and Enumeration Detection
- 4.9.4 Resource Consumption and Availability Abuse Detection
- 4.9.5 Malicious Payload and API Exploit Detection
5 MARKET SIZE AND GROWTH FORECASTS (VALUES)
- 5.1 By Component
- 5.1.1 Solutions
- 5.1.2 Services
- 5.2 By Deployment
- 5.2.1 Cloud
- 5.2.2 On-Premises
- 5.2.3 Hybrid
- 5.3 By Organization Size
- 5.3.1 Large Enterprises
- 5.3.2 Small and Medium-Sized Enterprises
- 5.4 By API Type
- 5.4.1 REST APIs
- 5.4.2 GraphQL APIs
- 5.4.3 SOAP APIs
- 5.4.4 gRPC and Other APIs
- 5.5 By Industry Vertical
- 5.5.1 Government and Public Administration
- 5.5.2 Industrial Manufacturing
- 5.5.3 Retail and E-Commerce
- 5.5.4 Transportation and Logistics
- 5.5.5 Energy and Utilities
- 5.5.6 Oil and Gas
- 5.5.7 IT and Telecommunication
- 5.5.8 Media and Entertainment
- 5.5.9 Education and Research Institutions
- 5.5.10 Healthcare and Life Sciences
- 5.5.11 Banking, Financial Services, and Insurance (BFSI)
- 5.5.12 Other Industry Verticals
- 5.6 By Geography
- 5.6.1 North America
- 5.6.1.1 United States
- 5.6.1.2 Canada
- 5.6.1.3 Mexico
- 5.6.2 South America
- 5.6.2.1 Brazil
- 5.6.2.2 Argentina
- 5.6.2.3 Rest of South America
- 5.6.3 Europe
- 5.6.3.1 Germany
- 5.6.3.2 United Kingdom
- 5.6.3.3 France
- 5.6.3.4 Italy
- 5.6.3.5 BENELUX
- 5.6.3.6 Rest of Europe
- 5.6.4 Asia-Pacific
- 5.6.4.1 China
- 5.6.4.2 Japan
- 5.6.4.3 India
- 5.6.4.4 South Korea
- 5.6.4.5 Australia
- 5.6.4.6 Rest of Asia-Pacific
- 5.6.5 Middle East and Africa
- 5.6.5.1 Middle East
- 5.6.5.1.1 United Arab Emirates
- 5.6.5.1.2 Saudi Arabia
- 5.6.5.1.3 Rest of Middle East
- 5.6.5.2 Africa
- 5.6.5.2.1 South Africa
- 5.6.5.2.2 Nigeria
- 5.6.5.2.3 Egypt
- 5.6.5.2.4 Rest of Africa
- 5.6.5.1 Middle East
- 5.6.1 North America
6 COMPETITIVE LANDSCAPE
- 6.1 Market Concentration
- 6.2 Strategic Moves
- 6.3 Market Share Analysis
- 6.4 Company Profiles (includes Global Level Overview, Market Level Overview, Core Segments, Financials as available, Strategic Information, Market Rank/Share, Products and Services, Recent Developments)
- 6.4.1 42Crunch
- 6.4.2 Akamai Technologies, Inc.
- 6.4.3 Akto Security Inc.
- 6.4.4 AppSentinels, Inc.
- 6.4.5 APISec.ai, Inc.
- 6.4.6 Arkose Labs Inc.
- 6.4.7 Cequence Security, Inc.
- 6.4.8 Cloudflare, Inc.
- 6.4.9 Data Theorem, Inc.
- 6.4.10 F5, Inc.
- 6.4.11 Fastly, Inc.
- 6.4.12 FireTail, Inc.
- 6.4.13 Imperva, Inc.
- 6.4.14 Indusface Private Limited
- 6.4.15 Levo, Inc.
- 6.4.16 Noname Security, Inc.
- 6.4.17 Salt Security, Inc.
- 6.4.18 SecureBlink, Inc.
- 6.4.19 Traceable, Inc.
- 6.4.20 Wallarm, Inc.
- 6.4.21 Kong Inc.
- 6.4.22 Wiz, Inc.
- 6.4.23 Zimperium, Inc.
- 6.4.24 Zscaler, Inc.
- 6.4.25 Radware Ltd.
7 MARKET OPPORTUNITIES AND FUTURE TRENDS
- 7.1 White-Space and Unmet-Need Assessment
- 7.2 Future Outlook

