PUBLISHER: Mordor Intelligence | PRODUCT CODE: 2185173

PUBLISHER: Mordor Intelligence | PRODUCT CODE: 2185173
Post-Quantum Cryptography Migration Services - Market Share Analysis, Industry Trends & Statistics, Growth Forecasts (2027 - 2032)
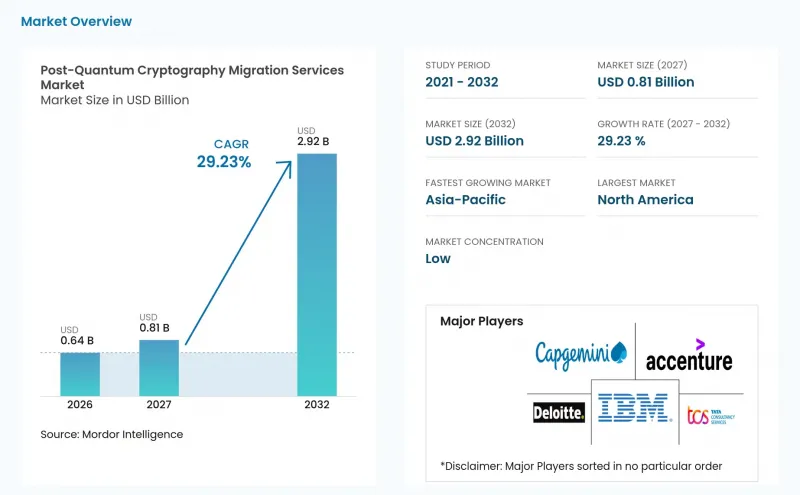
According to Mordor Intelligence, the post-quantum cryptography migration services market size is projected to expand from USD 0.64 billion in 2026 and USD 0.81 billion in 2027 to USD 2.92 billion by 2032, registering a CAGR of 29.23% between 2027 to 2032.
Global Post-Quantum Cryptography Migration Services Market Trends and Insights
Finalization of NIST PQC Standards and Government Migration Timelines
NIST finalized FIPS 203 for ML-KEM, FIPS 204 for ML-DSA, and FIPS 205 for SLH-DSA, giving organizations a defined baseline for migration planning. NIST also selected HQC as a candidate for additional standardization in March 2025. These standards allow security teams to replace general planning with testing, architecture decisions, and supplier selection. The European Commission's coordinated roadmap calls for member states to begin the transition by the end of 2026 and complete transitions for high-risk use cases by 2030. The post-quantum cryptography migration services market is therefore driven by a shift from optional readiness activities to programs requiring documented milestones. Contractors and suppliers can also be drawn into the work when public procurement requirements make quantum-safe capability a condition of participation.
Harvest-Now-Decrypt-Later Risk for Long-Lived Sensitive Data
Harvest-now-decrypt-later risk arises when an adversary stores encrypted traffic or data now and waits for a future capability to break the underlying public-key protection. Europol has urged financial services organizations to prioritize post-quantum migration activity because the risk applies to data with long confidentiality requirements. A Federal Reserve paper examined this risk in distributed ledger networks and noted that later decryption can permanently expose previously recorded information. Financial institutions, health care organizations, and public bodies face greater exposure where records must remain confidential for many years. This condition makes cryptographic inventory and data classification central parts of the post-quantum cryptography migration services market. It also favors migration sequencing that first protects data with the longest confidentiality life.
Shortage of Specialized PQC Engineering and Migration Talent
The number of professionals capable of executing post-quantum migration in large, complex environments remains limited. Financial services institutions have reported both insufficient specialized skills and unclear internal ownership of cryptographic transition programs. Migration requires knowledge of cryptography, software engineering, network protocols, PKI, hardware security modules, and governance. This combination makes it difficult for organizations to staff programs entirely with internal personnel. The constraint can slow execution in the near term, particularly in North America and Europe, where early programs compete for scarce specialists. It can also sustain demand in the post-quantum cryptography migration services market for managed services and multi-year operational support.
Other drivers and restraints analyzed in the detailed report include:
- Cryptographic Debt Across Cloud, PKI, and Distributed Applications
- Expansion of Digital Identity, Payments, and Connected Infrastructure
- Legacy Dependencies and Interoperability Constraints
For complete list of drivers and restraints, kindly check the Table Of Contents.
Segment Analysis
Cryptographic Discovery, Inventory, and Risk Prioritization held 24.73% of revenue in 2026. Organizations cannot sequence a migration before identifying where vulnerable algorithms, certificates, libraries, and protocols are used. Discovery engagements assess source repositories, certificate authorities, HSMs, cloud key management services, and network endpoints. The work creates a Cryptographic Bill of Materials that links applications and infrastructure to cryptographic dependencies. Strategy, Governance, and Migration Roadmapping supports early decisions on ownership, policy, risk ranking, and budget allocation. Testing, Validation, and Performance Optimization then confirms that candidate controls can operate in production-like settings.
PQC Algorithm Integration and Remediation is projected to expand at a 31.28% CAGR through 2032. Customers that completed early discovery and planning work in 2025 and 2026 can move into algorithm replacement and library-level remediation. This phase may include updates to APIs, software dependencies, key exchange methods, signing workflows, and security policies. PKI, Certificate, and Digital Identity Migration remains an important related service because organizations must retire vulnerable certificate hierarchies and issue replacement credentials across large device fleets. Microsoft has advised organizations to inventory certificate dependencies and build non-production environments for post-quantum testing. The post-quantum cryptography migration services industry therefore requires providers to carry work from assessment through controlled deployment.
Applications and Source Code accounted for 27.41% of the post-quantum cryptography migration services market in 2026. Software-layer cryptography is widely deployed and can often be addressed through library updates, code changes, and CI/CD controls. Application teams must identify any embedded dependencies on RSA, ECDSA, Diffie-Hellman, and certificate handling before making these changes. Cloud Workloads and Data Platforms are also important targets as infrastructure providers introduce hybrid key exchange support. AWS has documented approaches for migrating workloads and data protection services to quantum-resistant cryptography. HSM, Key Management and Secrets, as well as Networks and Secure Protocols, require more careful compatibility work because firmware and hardware lifecycles can limit available options.
PKI, Certificates, and Digital Identity are expected to expand at a 32.76% CAGR through 2032. Digital trust systems require migration options that maintain interoperability across browsers, devices, applications, and external partners. An IETF draft describes composite certificates, dual certificates, and standalone post-quantum certificates as distinct approaches with different implementation tradeoffs. Shorter certificate validity periods can increase the need for automated renewal while organizations introduce hybrid certificate profiles. This makes certificate lifecycle management a direct part of the migration path rather than a separate administrative task. The post-quantum cryptography migration services market offers opportunities where providers can integrate PKI planning, automated issuance, testing, and governance.
Complete Report Scope:
- By Service Type
- Strategy, Governance, and Migration Roadmapping
- Cryptographic Discovery, Inventory, and Risk Prioritization
- PQC Algorithm Integration and Remediation
- PKI, Certificate, and Digital Identity Migration
- Network, TLS, and Secure-Protocol Migration
- Testing, Validation, and Performance Optimization
- Other Services
- By Migration Target
- Applications and Source Code
- PKI, Certificates and Digital Identity
- Networks and Secure Protocols
- Cloud Workloads and Data Platforms
- HSM, Key Management and Secrets
- Other Migration Targets
- By Deployment Model
- Cloud-Based
- On-Premises
- Hybrid
- By Organization Size
- Large Enterprises
- Small and Medium Enterprises
- By End-User Industry
- Banking, Financial Services, and Insurance (BFSI)
- IT and Telecommunications
- Government and Public Administration
- Healthcare and Medical Devices
- Energy and Utilities
- Other End-User Industries
- By Geography
- North America
- United States
- Canada
- South America
- Brazil
- Mexico
- Rest of South America
- Europe
- United Kingdom
- Germany
- France
- Italy
- Rest of Europe
- Asia-Pacific
- China
- Japan
- South Korea
- India
- Australia and New Zealand
- Rest of Asia-Pacific
- Middle East
- Israel
- Saudi Arabia
- United Arab Emirates
- Rest of Middle East
- Africa
- South Africa
- Rest of Africa
- North America
Geography Analysis
North America held 41.67% of the post-quantum cryptography migration services market share in 2026. The region combines federal security activity, defense procurement, financial-sector demand, major cloud platforms, and a concentration of specialist vendors. SandboxAQ announced a five-year agreement with the Department of War CIO in December 2025 to deploy AQtive Guard for cryptographic discovery across systems. The concentration of IT services firms and cryptographic technology providers gives organizations access to a broad range of implementation options. It also raises competitive pressure among providers that seek federal and critical-infrastructure work.
Europe has a strong policy basis for the post-quantum cryptography migration services market. The European Commission's coordinated roadmap sets out an expectation of beginning transition activities by the end of 2026. Germany's BSI issued its January 2026 update on cryptographic mechanisms and key lengths. The Digital Operational Resilience Act also places cyber resilience responsibilities on financial entities. These conditions create demand for migration planning that can be aligned with supervision, supplier relationships, and existing risk controls. South America, the Middle East, and Africa remain earlier-stage areas, with initial opportunities linked to public-sector, financial-services, and energy programs.
Asia-Pacific is projected to expand at a 32.94% CAGR through 2032. South Korea demonstrated 16 cryptographic modules and 19 quantum-resistant transition cases through a national pilot in December 2025. Domestic standards, cloud infrastructure expansion, and state-backed technology programs can create localized service requirements. Japan's cybersecurity and post-quantum cryptography agenda has identified the protection of sensitive data and critical systems as an important priority. India has also published a quantum-safe ecosystem document that discusses a national approach for critical infrastructure. These developments support service models that can adapt global standards to national algorithms, local regulations, and regional technology ecosystems.
- International Business Machines Corporation
- Accenture plc
- Capgemini SE
- Deloitte Touche Tohmatsu Limited
- Tata Consultancy Services Limited
- PwC International Limited
- KPMG International Cooperative
- Ernst & Young Global Limited
- Thales S.A.
- Entrust Corporation
- SandboxAQ LLC
- PQShield Limited
- QuSecure, Inc.
- Keyfactor, Inc.
- DigiCert, Inc.
- ISARA Corporation
- CryptoNext Security
- Microsoft Corporation
- Amazon Web Services, Inc.
- Google LLC
- Cloudflare, Inc.
- NTT DATA Corporation
- HCLTech
- Wipro Limited
- Infosys Limited
- Eviden
- Quantinuum Ltd.
- NXP Semiconductors N.V.
Additional Benefits:
- The market estimate (ME) sheet in Excel format
- 3 months of analyst support
TABLE OF CONTENTS
1 INTRODUCTION
- 1.1 Study Assumptions and Market Definition
- 1.2 Scope of the Study
2 RESEARCH METHODOLOGY
3 EXECUTIVE SUMMARY
4 MARKET LANDSCAPE
- 4.1 Market Overview
- 4.2 Market Drivers
- 4.2.1 Finalization of NIST PQC Standards and Government Migration Timelines
- 4.2.2 Harvest-Now-Decrypt-Later Risk for Long-Lived Sensitive Data
- 4.2.3 Cryptographic Debt Across Cloud, PKI and Distributed Applications
- 4.2.4 Expansion of Digital Identity, Payments and Connected Infrastructure
- 4.2.5 Cryptographic Bill of Materials and Continuous Discovery Adoption
- 4.2.6 Supplier-Level Cryptography Visibility as an Under-Reported Procurement Requirement
- 4.3 Market Restraints
- 4.3.1 Shortage of Specialized PQC Engineering and Migration Talent
- 4.3.2 Legacy Dependencies and Interoperability Constraints
- 4.3.3 Larger Keys, Signatures and Protocol Messages Increase Performance Burden
- 4.3.4 Unclear Accountability for Cryptography Embedded in Third-Party and Open-Source Components
- 4.4 Impact of Macroeconomic Factors on the Market
- 4.5 Industry Value Chain Analysis
- 4.6 Regulatory Landscape
- 4.7 Technological Outlook
- 4.8 Porter's Five Forces Analysis
- 4.8.1 Threat of New Entrants
- 4.8.2 Bargaining Power of Suppliers
- 4.8.3 Bargaining Power of Buyers
- 4.8.4 Threat of Substitutes
- 4.8.5 Competitive Rivalry
5 MARKET SIZE AND GROWTH FORECASTS (VALUE)
- 5.1 By Service Type
- 5.1.1 Strategy, Governance, and Migration Roadmapping
- 5.1.2 Cryptographic Discovery, Inventory, and Risk Prioritization
- 5.1.3 PQC Algorithm Integration and Remediation
- 5.1.4 PKI, Certificate, and Digital Identity Migration
- 5.1.5 Network, TLS, and Secure-Protocol Migration
- 5.1.6 Testing, Validation, and Performance Optimization
- 5.1.7 Other Services
- 5.2 By Migration Target
- 5.2.1 Applications and Source Code
- 5.2.2 PKI, Certificates and Digital Identity
- 5.2.3 Networks and Secure Protocols
- 5.2.4 Cloud Workloads and Data Platforms
- 5.2.5 HSM, Key Management and Secrets
- 5.2.6 Other Migration Targets
- 5.3 By Deployment Model
- 5.3.1 Cloud-Based
- 5.3.2 On-Premises
- 5.3.3 Hybrid
- 5.4 By Organization Size
- 5.4.1 Large Enterprises
- 5.4.2 Small and Medium Enterprises
- 5.5 By End-User Industry
- 5.5.1 Banking, Financial Services, and Insurance (BFSI)
- 5.5.2 IT and Telecommunications
- 5.5.3 Government and Public Administration
- 5.5.4 Healthcare and Medical Devices
- 5.5.5 Energy and Utilities
- 5.5.6 Other End-User Industries
- 5.6 By Geography
- 5.6.1 North America
- 5.6.1.1 United States
- 5.6.1.2 Canada
- 5.6.2 South America
- 5.6.2.1 Brazil
- 5.6.2.2 Mexico
- 5.6.2.3 Rest of South America
- 5.6.3 Europe
- 5.6.3.1 United Kingdom
- 5.6.3.2 Germany
- 5.6.3.3 France
- 5.6.3.4 Italy
- 5.6.3.5 Rest of Europe
- 5.6.4 Asia-Pacific
- 5.6.4.1 China
- 5.6.4.2 Japan
- 5.6.4.3 South Korea
- 5.6.4.4 India
- 5.6.4.5 Australia and New Zealand
- 5.6.4.6 Rest of Asia-Pacific
- 5.6.5 Middle East
- 5.6.5.1 Israel
- 5.6.5.2 Saudi Arabia
- 5.6.5.3 United Arab Emirates
- 5.6.5.4 Rest of Middle East
- 5.6.6 Africa
- 5.6.6.1 South Africa
- 5.6.6.2 Rest of Africa
- 5.6.1 North America
6 COMPETITIVE LANDSCAPE
- 6.1 Market Concentration
- 6.2 Strategic Moves
- 6.3 Market Share Analysis
- 6.4 Company Profiles (includes Global Level Overview, Market Level Overview, Core Segments, Financials as available, Strategic Information, Market Rank/Share, Products and Services, Recent Developments)
- 6.4.1 International Business Machines Corporation
- 6.4.2 Accenture plc
- 6.4.3 Capgemini SE
- 6.4.4 Deloitte Touche Tohmatsu Limited
- 6.4.5 Tata Consultancy Services Limited
- 6.4.6 PwC International Limited
- 6.4.7 KPMG International Cooperative
- 6.4.8 Ernst & Young Global Limited
- 6.4.9 Thales S.A.
- 6.4.10 Entrust Corporation
- 6.4.11 SandboxAQ LLC
- 6.4.12 PQShield Limited
- 6.4.13 QuSecure, Inc.
- 6.4.14 Keyfactor, Inc.
- 6.4.15 DigiCert, Inc.
- 6.4.16 ISARA Corporation
- 6.4.17 CryptoNext Security
- 6.4.18 Microsoft Corporation
- 6.4.19 Amazon Web Services, Inc.
- 6.4.20 Google LLC
- 6.4.21 Cloudflare, Inc.
- 6.4.22 NTT DATA Corporation
- 6.4.23 HCLTech
- 6.4.24 Wipro Limited
- 6.4.25 Infosys Limited
- 6.4.26 Eviden
- 6.4.27 Quantinuum Ltd.
- 6.4.28 NXP Semiconductors N.V.
7 MARKET OPPORTUNITIES AND FUTURE OUTLOOK
- 7.1 White-Space and Unmet-Need Assessment
- 7.2 Future Outlook to 2032

