PUBLISHER: Mordor Intelligence | PRODUCT CODE: 2120614

PUBLISHER: Mordor Intelligence | PRODUCT CODE: 2120614
India Network Security And Cyber Risk Management - Market Share Analysis, Industry Trends & Statistics, Growth Forecasts (2026 - 2031)
According to Mordor Intelligence, the India network security and cyber risk management market size is expected to grow from USD 760 million in 2025 to USD 872.3 million in 2026 and is forecast to reach USD 1.74 billion by 2031 at 14.78% CAGR over 2026-2031.
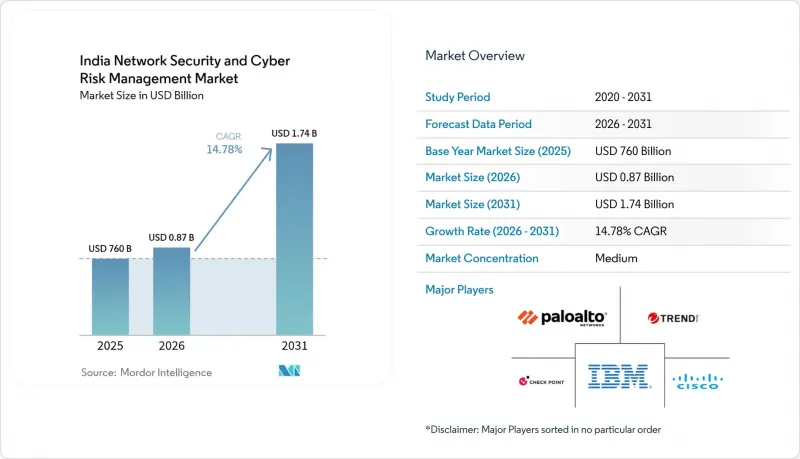
This report is Segmented by Segment (Security Information and Event Management (SIEM), and More), Solution (Encryption, Identity and Access Management (IAM), and More), Service (Network Security, and More), End-User Industry (BFSI, Government and Defence, and More), and Deployment Mode (On-Premise, and More). The Market Forecasts are Provided in Terms of Value (USD).
India Network Security And Cyber Risk Management Market Trends and Insights
FinTech Transaction-Sprawl Intensifying Attack Surface
Indian FinTech platforms recorded 429,847 cyber incidents in 2023, with exploits frequently targeting open APIs and third-party integrations that multiply entry points for attackers. The Aditya Birla Capital breach, which siphoned USD 0.23 million in digital gold, illustrates cascading risks created by interconnected service providers. Compliance with DPDP 2023 demands encryption, audit trails and breach notification, pushing FinTechs toward advanced SIEM platforms with AI-based anomaly detection. Competitive pressures encourage rapid feature releases, yet every new integration widens the attack surface. Consequently, chief information security officers prioritize continuous monitoring, micro-segmentation and identity-centric controls to protect customer transactions and sustain trust across the India network security and cyber risk management market.
Zero-Day Supply-Chain Exploits on Indian OEM Firmware
CERT-In has flagged multiple critical vulnerabilities in local OEM firmware, including Samsung devices running Android 11-14, enabling arbitrary code execution and sensitive-data exfiltration . A 2024 ransomware campaign against Indian banks leveraged CVE-2024-23897 embedded in Jenkins servers to breach payment gateways, underscoring how firmware flaws propagate across supply chains . Proliferation of Industry 4.0 devices magnifies this exposure, especially in export-oriented manufacturing hubs. Enterprises, therefore, embed firmware-integrity checks, vendor-audit scorecards, and continuous vulnerability scanning in procurement workflows. Tightening supply-chain security raises demand for endpoint detection and response tools integrated with SIEM and SOAR platforms, reinforcing growth in the India network security and cyber risk management market.
Shortage of 400k Skilled Cyber-Security Professionals
India requires 1 million cybersecurity professionals by 2027, yet only 300,000 people currently possess employable skills, creating a 400,000-person gap. BFSI alone accounts for half of this unmet demand, which raises labor costs and stretches internal teams . Organizations increasingly outsource to Managed Detection and Response providers and deploy AI-based automation to compensate for missing talent. Government initiatives like Microsoft's CyberShikshaa upskill underrepresented groups, yet annual output remains below market needs. Skills scarcity thereby slows implementation of sophisticated architectures such as zero-trust among small and mid-size enterprises, tempering the growth trajectory of the India network security and cyber risk management market.
Other drivers and restraints analyzed in the detailed report include:
- Mandatory CERT-In Six-Hour Breach-Reporting Rule
- Rising Cloud-Native Adoption Among MSMEs
- Fragmented State-Level Data-Protection Enforcement
For complete list of drivers and restraints, kindly check the Table Of Contents.
Segment Analysis
The SIEM segment generated 28.12% of the India network security and cyber risk management market size in 2025, reflecting organizations' need for centralized log analytics and automated alerts that satisfy CERT-In mandates. Large enterprises integrate SIEM with SOAR to orchestrate playbooks, reducing response times and audit overhead. Mid-sized firms prefer cloud-hosted SIEM subscriptions to avoid capital expenditure. Meanwhile, IGA solutions compound at a 17.18% CAGR as identity becomes the new perimeter in hybrid workplaces. Automated provisioning and risk-based access reviews improve user-lifecycle efficiency and compliance reporting.
Growth in both segments stems from demand for unified visibility in multi-cloud environments. Vendors embed machine-learning models for anomaly detection, while marketplace integrations pull telemetry from SaaS, container and IoT layers. As digital supply chains deepen, customers favor platforms that combine SIEM, XDR and identity governance, signaling a shift toward converged security operations that will redefine the India network security and cyber risk management market.
Identity and Access Management retained a 31.05% share of the India network security and cyber risk management market in 2025, anchoring everything from privileged-access controls to single sign-on. Regulatory clauses requiring granular access logs further entrench IAM platforms. Yet Zero Trust Network Access posts the fastest 18.05% CAGR, propelled by remote-work policies and 5G edge connectivity. ZTNA replaces perimeter-based VPNs with continuous verification, micro-segmentation, and contextual policies.
Encryption and DLP gain traction as enterprises prepare for post-quantum threats and DPDP compliance, respectively. Buyers increasingly adopt solution suites that integrate IAM, ZTNA, and encryption under unified policy engines. This convergence reduces operational overhead and accelerates adoption among MSMEs, expanding revenue opportunities across the India network security and cyber risk management market.
Complete Report Scope:
- By Segment
- Security Information and Event Management (SIEM)
- Secure Web Gateway (SWG)
- Identity Governance and Administration (IGA)
- Enterprise Content-Aware Data Loss Prevention (DLP)
- By Solution
- Encryption
- Identity and Access Management (IAM)
- Data Loss Protection (DLP)
- Intrusion Detection/Prevention (IDS/IPS)
- Zero-Trust Network Access (ZTNA)
- By Service
- Network Security
- Endpoint Security
- Wireless Security
- Cloud Security
- Managed Detection and Response (MDR)
- By End-user Industry
- BFSI
- Government and Defence
- Healthcare
- IT and Telecom
- Retail and E-Commerce
- Manufacturing
- By Deployment Mode
- On-premise
- Cloud-based
List of Companies Covered in this Report:
- Cisco Systems Inc.
- Palo Alto Networks Inc.
- IBM Corporation
- Check Point Software Technologies Ltd.
- Trend Micro Inc.
- Fortinet Inc.
- Sophos Group plc
- Safe Security (Safe Security Pvt Ltd., formerly Lucideus)
- Quick Heal Technologies Ltd.
- Tata Communications Ltd.
- Wipro Ltd. (Cybersecurity and Risk Services)
- HCL Technologies Ltd.
- Infosys Ltd.
- Instasafe Technologies Pvt Ltd.
- XenArmor Security Solutions
- ArrayShield Technologies Pvt Ltd.
- Data Resolve Technologies Pvt Ltd.
- Netrika Consulting India Pvt Ltd.
- Mirox Cybersecurity and Technology Pvt Ltd.
- Cyberoam Technologies Pvt Ltd. (a Sophos Company)
Additional Benefits:
- The market estimate (ME) sheet in Excel format
- 3 months of analyst support
TABLE OF CONTENTS
1 INTRODUCTION
- 1.1 Market Definition and Study Assumptions
- 1.2 Scope of the Study
2 RESEARCH METHODOLOGY
3 EXECUTIVE SUMMARY
4 MARKET LANDSCAPE
- 4.1 Market Overview
- 4.2 Market Drivers
- 4.2.1 FinTech transaction-sprawl intensifying attack surface
- 4.2.2 Zero-day supply-chain exploits on Indian OEM firmware
- 4.2.3 Mandatory CERT-In six-hour breach-reporting rule
- 4.2.4 Rising cloud-native adoption among MSMEs
- 4.2.5 5G private?network roll-outs in smart-manufacturing hubs
- 4.2.6 Generative-AI driven phishing and deep-fake prevention spend
- 4.3 Market Restraints
- 4.3.1 Shortage of 400k skilled cyber-security professionals
- 4.3.2 Fragmented state-level data-protection enforcement
- 4.3.3 High TCO of zero-trust architectures for SMEs
- 4.3.4 Legacy OT systems in critical infrastructure
- 4.4 Value Chain Analysis
- 4.5 Evaluation of Critical Regulatory Framework
- 4.6 Impact Assessment of Key Stakeholders
- 4.7 Technological Outlook
- 4.8 Porter's Five Forces Analysis
- 4.8.1 Bargaining Power of Suppliers
- 4.8.2 Bargaining Power of Consumers
- 4.8.3 Threat of New Entrants
- 4.8.4 Threat of Substitutes
- 4.8.5 Intensity of Competitive Rivalry
- 4.9 Impact of Macro-economic Factors
5 MARKET SIZE AND GROWTH FORECASTS (VALUE)
- 5.1 By Segment
- 5.1.1 Security Information and Event Management (SIEM)
- 5.1.2 Secure Web Gateway (SWG)
- 5.1.3 Identity Governance and Administration (IGA)
- 5.1.4 Enterprise Content-Aware Data Loss Prevention (DLP)
- 5.2 By Solution
- 5.2.1 Encryption
- 5.2.2 Identity and Access Management (IAM)
- 5.2.3 Data Loss Protection (DLP)
- 5.2.4 Intrusion Detection/Prevention (IDS/IPS)
- 5.2.5 Zero-Trust Network Access (ZTNA)
- 5.3 By Service
- 5.3.1 Network Security
- 5.3.2 Endpoint Security
- 5.3.3 Wireless Security
- 5.3.4 Cloud Security
- 5.3.5 Managed Detection and Response (MDR)
- 5.4 By End-user Industry
- 5.4.1 BFSI
- 5.4.2 Government and Defence
- 5.4.3 Healthcare
- 5.4.4 IT and Telecom
- 5.4.5 Retail and E-Commerce
- 5.4.6 Manufacturing
- 5.5 By Deployment Mode
- 5.5.1 On-premise
- 5.5.2 Cloud-based
6 COMPETITIVE LANDSCAPE
- 6.1 Market Concentration
- 6.2 Strategic Moves
- 6.3 Market Share Analysis
- 6.4 Company Profiles (includes Global level Overview, Market level overview, Core Segments, Financials as available, Strategic Information, Market Rank/Share for key companies, Products and Services, and Recent Developments)
- 6.4.1 Cisco Systems Inc.
- 6.4.2 Palo Alto Networks Inc.
- 6.4.3 IBM Corporation
- 6.4.4 Check Point Software Technologies Ltd.
- 6.4.5 Trend Micro Inc.
- 6.4.6 Fortinet Inc.
- 6.4.7 Sophos Group plc
- 6.4.8 Safe Security (Safe Security Pvt Ltd., formerly Lucideus)
- 6.4.9 Quick Heal Technologies Ltd.
- 6.4.10 Tata Communications Ltd.
- 6.4.11 Wipro Ltd. (Cybersecurity and Risk Services)
- 6.4.12 HCL Technologies Ltd.
- 6.4.13 Infosys Ltd.
- 6.4.14 Instasafe Technologies Pvt Ltd.
- 6.4.15 XenArmor Security Solutions
- 6.4.16 ArrayShield Technologies Pvt Ltd.
- 6.4.17 Data Resolve Technologies Pvt Ltd.
- 6.4.18 Netrika Consulting India Pvt Ltd.
- 6.4.19 Mirox Cybersecurity and Technology Pvt Ltd.
- 6.4.20 Cyberoam Technologies Pvt Ltd. (a Sophos Company)
7 MARKET OPPORTUNITIES AND FUTURE TRENDS
- 7.1 White-space and Unmet-need Assessment

